

AI agents drive new cyber risk, Keeper Security warns
Thu, 1st Oct 2026 (Today)
Keeper Security executives warn that artificial intelligence is reshaping cyber risk by multiplying digital identities and creating new routes to privileged access. Their comments come as organisations and consumers mark Cybersecurity Awareness Month amid rising concern over AI-driven attacks.
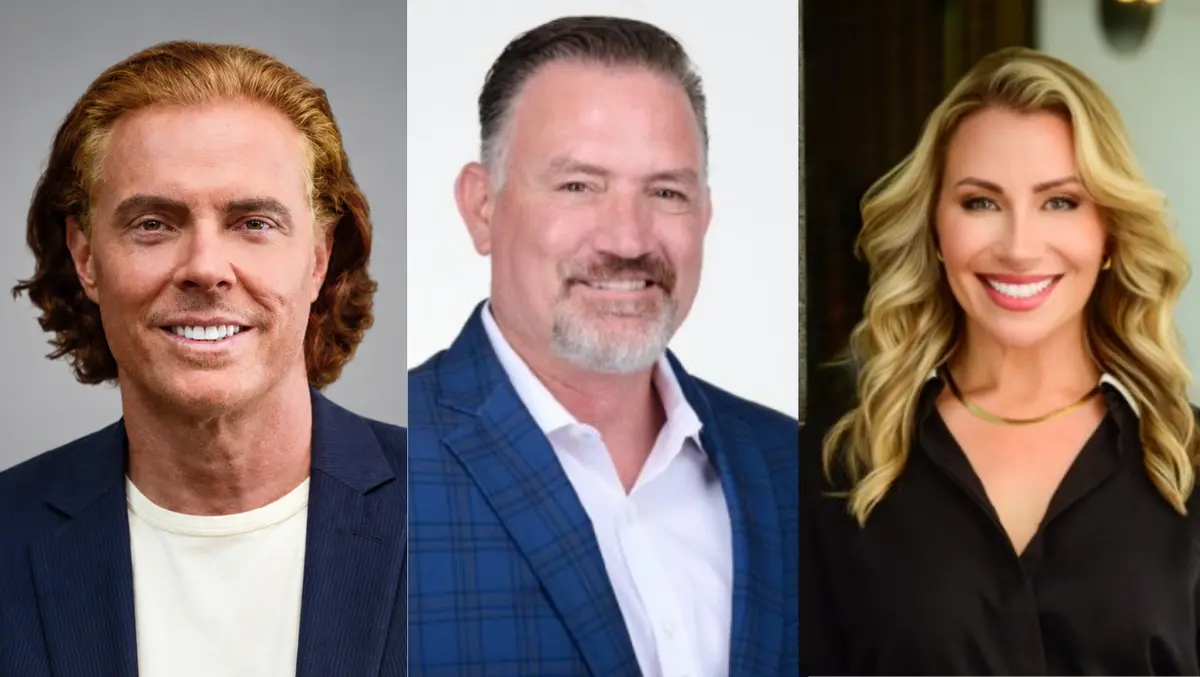
Chief Executive Officer and Co-Founder Darren Guccione said organisations are rapidly deploying AI agents across business environments. These systems now act as a new layer of digital users, interacting with core infrastructure and data.
He said companies often treat these agents differently from human staff in identity governance and access control, increasing the risk of unmanaged privileges and long-lived credentials.
"Cybersecurity Awareness Month has traditionally focused on human behavior: recognizing phishing, protecting credentials and making better decisions about access to an organization's network, data and accounts. That conversation now needs to expand. As organizations rapidly deploy AI agents across their environments, they are creating an entirely new class of digital users, often without applying the same identity governance expected for employees, contractors or administrators.
"AI is transforming from intelligence to embedded enterprise infrastructure. AI agents can now authenticate into systems, retrieve sensitive information, interact with applications, execute workflows and make critical decisions - all at machine speed. If an agent has credentials and permissions, it represents an identity, and every identity creates risk when its access is excessive, persistent or poorly monitored.
"The biggest problem is scale. Organisations can deploy hundreds or thousands of non-human identities far faster than they onboard human employees. If those agents receive standing credentials, broad permissions or long-lived secrets without appropriate governance, the attack surface expands just as quickly. A compromised AI agent with privileged access can give an attacker direct access to critical systems and data.
"The security principles needed to secure these identities are not new. Organisations should apply the same zero-trust discipline to AI agents that they apply to people: verify every identity, enforce the principle of least privilege, eliminate unnecessary standing access, continuously monitor privileged activity, and protect and rotate credentials and secrets. Access should be granted only to the resources required for a specific task and only for as long as necessary.
Cybersecurity awareness must evolve alongside technology. We have spent years teaching organizations that every employee identity requires governance. Now we need to extend that understanding to machines. The next frontier of cybersecurity awareness is recognizing that AI agents are users too. Organisations that govern them accordingly will be far better positioned to capture the benefits of agentic AI without creating an unmanaged layer of privileged access," said Darren Guccione, Chief Executive Officer and Co-Founder of Keeper Security.
The comments reflect growing industry focus on so-called non-human identities in corporate networks. Security teams report that automation, machine accounts and software agents now hold large volumes of credentials and secrets across hybrid and cloud estates.
Michael Marino, Senior Vice President of Strategy, Identity Security at Keeper Security, said privileged access has shifted with this change in infrastructure. Traditional models built around administrator password vaults no longer match how businesses operate, he said.
He pointed to the growth of cloud and remote work, as well as the mix of employees, contractors, applications and service accounts that now require different permission levels. Modern Privileged Access Management, or PAM, must address the timing and scope of access as well as session monitoring, he said.
Keeper research cited by Marino found that 94% of organisations now operate in hybrid or cloud-first environments. That distribution of systems has dissolved fixed network perimeters and spread sensitive access across many services.
Least privilege and just-in-time access now sit at the centre of PAM strategy, Marino said. Security teams are working to remove standing administrative rights and replace them with temporary, auditable elevation.
He also linked the next phase of PAM to automation and AI on both sides of the security divide, saying AI agents are creating privileged access at a scale that is difficult to manage manually.
AI tools can also examine large volumes of privileged activity and flag anomalies faster than human analysts, he said, framing this as an adaptation of security fundamentals rather than a wholesale replacement.
"Cybersecurity Awareness Month is an opportunity to reflect not only on how cyber threats have evolved, but on how our defenses have had to evolve alongside them. Over my career in identity security, I've seen few areas change as significantly as Privileged Access Management (PAM).
"PAM was once primarily about putting administrator passwords into a secure vault. That made sense when infrastructure was largely on-premises, privileged users were relatively easy to identify and access occurred within clearly defined network boundaries. The objective was straightforward: protect powerful credentials and maintain an audit trail around their use.
"The days of a contained network perimeter no longer exist. Organisations now operate across cloud, hybrid and remote infrastructure, while employees, contractors, applications, service accounts and automated systems all require different levels of access. Keeper research found that 94% of organizations operate in hybrid or cloud-first environments.* As access has become more distributed, the traditional concept of privilege has expanded with it.
"Modern PAM, therefore, has to be about much more than protecting passwords. It must control when privileged access is granted, what someone or something can access, and what happens during that session. Principles such as least privilege, just-in-time access and zero standing privilege help organizations replace persistent administrative rights with access that is intentional, temporary and auditable.
"The next stage of this evolution will be driven by automation and AI. Non-human identities and AI agents are creating privileged access at a scale that security teams cannot manage manually. At the same time, AI can help defenders analyze privileged activity and identify suspicious behavior much faster.
The lesson for Cybersecurity Awareness Month is that cybersecurity fundamentals don't disappear as technology changes - they evolve to meet the occasion. Privileged access will always represent concentrated risk. Effective PAM is about continually adapting how that risk is controlled as the identities, infrastructure and technologies around it change," said Michael Marino, Senior Vice President of Strategy, Identity Security at Keeper Security.
Alongside corporate concerns, Keeper Security highlighted consumer risks from AI-generated media. Cybersecurity Expert Anne Cutler said deepfakes now sit at the intersection of personal identity, fraud and social engineering.
Synthetic audio and video can make phishing attempts appear more authentic and targeted, she said. Criminals use these tools to imitate familiar voices or images and increase pressure on victims.
Cutler urged individuals to treat unexpected contact from purported family members, colleagues or financial institutions with greater scepticism. Unusual or urgent requests should be verified through separate, trusted channels, she said.
She also advised against sharing passwords or multi-factor authentication codes in response to unsolicited approaches. Strong, unique credentials and multi-factor authentication remain a core part of account protection, she said.
"For many people, deepfakes still feel like an internet novelty - a fake celebrity video, an altered image or an amusing example of what AI can create. That perception needs to change. Deepfakes are increasingly relevant to personal cybersecurity because the same technology used for entertainment can be weaponized by cybercriminals to impersonate other people, manipulate trust and steal sensitive information.
"Cybercriminals have always relied on social engineering, but what AI changes is how convincing and scalable those attacks can become. An attacker no longer has to rely solely on a suspicious email pretending to be an organization or individual you know. AI can help imitate a person's voice, appearance or communication style, creating a much more persuasive request for money, account credentials or sensitive information. Our natural instinct to trust familiarity has become a vulnerability.
"Cybersecurity Awareness Month is an opportunity to update the way we think about personal security. Recognizing phishing emails remains important, but awareness now also means questioning unexpected requests regardless of how authentic or personal they appear. A familiar face or voice should no longer be treated as proof of identity.
"If a family member, colleague or financial institution appears to contact you with an unusual or urgent request, verify it through another trusted channel. Call the person using a number you already have rather than one provided in the message. Never provide passwords or Multi-Factor Authentication (MFA) codes in response to an unsolicited request, and always use strong, unique credentials backed up with MFA to make accounts harder to compromise.
Deepfake awareness is personal cybersecurity awareness. Understanding how attackers can weaponize synthetic media is becoming an essential part of protecting our identities, accounts and financial lives," said Anne Cutler, Cybersecurity Expert at Keeper Security.