
Graylog launches AI case system in security platform
Mon, 26th Oct 2026 (Today)
Graylog has launched the Verascend Incident System alongside version 7.2 of its security information and event management and log management platform, targeting security teams dealing with rising volumes of cyber alerts.
The product introduces a case-based approach to incident triage, instead of requiring analysts to review alerts one by one. It groups related evidence into prioritised cases, with AI agents carrying out an initial review before a human analyst investigates further.
The release comes as cybersecurity teams face pressure from a growing number of attacks, alongside staff and budget shortages. Graylog cited findings from the European Union Agency for Cybersecurity, ENISA, that ransomware operators are using AI coding assistants to build tools for affiliates. The FBI has also warned that cyberattacks are likely to increase as criminal groups industrialise ransomware, fraud and cryptocurrency theft.
Used by more than 60,000 organisations, the latest version of the platform is intended to help security teams focus on the incidents that present the greatest risk. Each case in Verascend opens with supporting evidence attached. Analysts can also run additional searches from within the case and receive an AI-assisted summary and suggested remediation steps when an investigation closes.
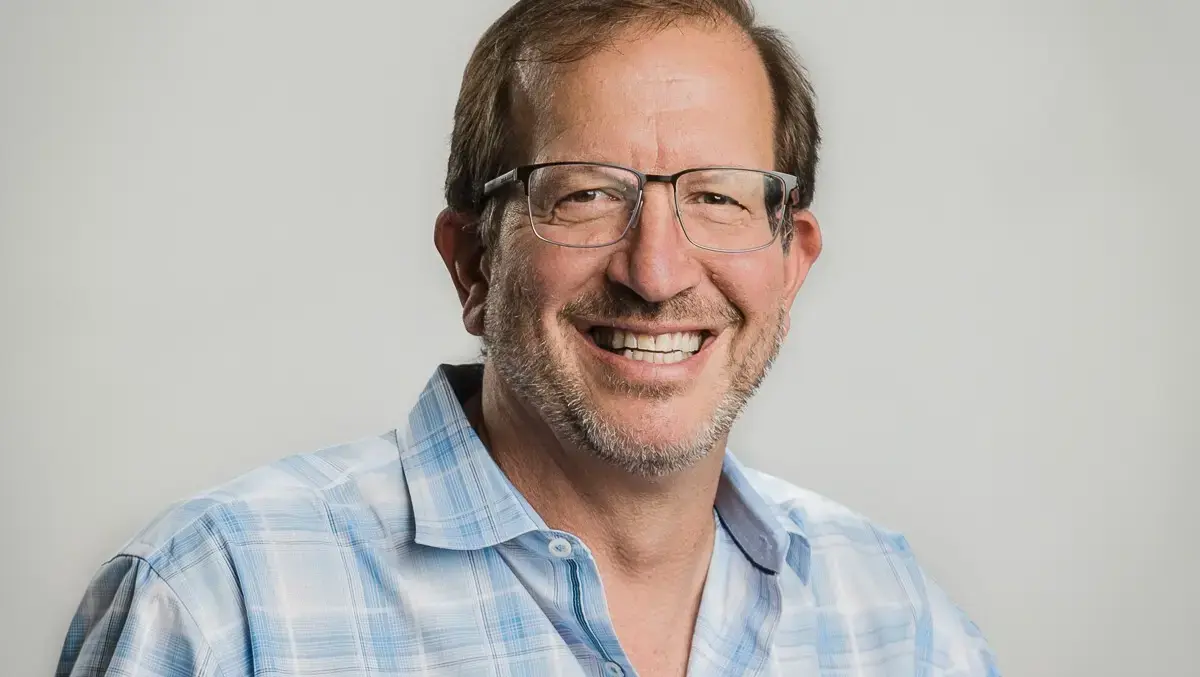
"Attackers are using AI to move faster, and most security teams are expected to keep up with a handful of people," said Andy Grolnick, Chief Executive Officer of Graylog.
"Hiring more analysts to read more alerts isn't a plan most of those teams can afford. With Verascend and Graylog v7.2, they start the day with verified cases instead of an overwhelming alert queue, and they keep their data where their regulators need it," Grolnick said.
Detection workflow
Verascend brings several of Graylog's existing detection methods into the same workflow. These include Detection Chains, which raise risk levels when further evidence supports signs of known adversary campaign activity, as well as Sigma rules and custom correlation rules, which now sit alongside other detection methods in a single case-management process.
A new Detection Chains page shows the threat actor associated with a campaign, along with targeted technologies and industries. Graylog also said expanded watchlists are aligned with its own detection content, allowing users to tune the system to their environment.
Seth Goldhammer, Vice President of Products at Graylog, said the system was designed so AI agents work from a narrower set of information after data has already been normalised and risk-scored.
"Most agentic SOC tools point an AI agent at raw log data and ask it to make sense of everything at once. We did it the other way around. Graylog normalises the data and scores the risk first, so by the time our agents get involved, they're reasoning over a small set of facts about a specific asset or user," Goldhammer said.
"That's why an analyst opens a case with the evidence already there - and can see every prompt and tool call behind the agent's assessment," he added.
System visibility
Version 7.2 also adds new views into pipeline performance, data lake storage and system health. These tools are intended to help platform administrators identify resource consumption, address bottlenecks and keep storage costs under control.
Graylog has also added support for OVH and Secunet SysEleven S3-compatible storage, giving European organisations an option to keep security data within the region without creating a separate storage architecture.
Data location is becoming a more prominent issue as security teams hand more triage work to AI systems. For European users in particular, data residency requirements have become an important factor in technology purchasing and deployment decisions.
Graylog said the Verascend Incident System is included in Graylog Security under existing licences. The company operates from offices in Hamburg, Houston, London and Singapore, and says its products are used in 180 countries.