
Qualys launches TruRisk Eliminate 2.0 with TruConfidence
Wed, 28th Oct 2026 (Today)
Qualys has launched TruRisk Eliminate 2.0 with TruConfidence. The product is now generally available.
The release adds a remediation intelligence and orchestration engine designed to automate more of the work involved in fixing cyber exposures. Qualys says the system supports what it calls Autonomous RemOps, combining patching, mitigation and rollout controls in a single workflow.
The launch comes as security teams face a shrinking gap between the discovery of software flaws and their exploitation. Qualys cited research showing that AI has cut that window from 32 days to five, increasing pressure on security and IT operations teams to move faster without disrupting services.
According to Qualys, the new version builds on data from half a billion patch deployments, with fewer than 0.1% resulting in rollbacks. It said 40% of those deployments were carried out autonomously. That history feeds into TruConfidence, which uses deployment data to help determine how fixes should be applied and in what order.
How it works
TruConfidence brings together several features introduced in recent quarters, including an AI-powered Patch Reliability Score, wave-based remediation managed by Agent Sara, peer-to-peer distribution and compensating controls based on prior patch activity. The aim is to help organisations decide whether to patch immediately, apply another fix or rely on protections already in place.
The system also extends remediation beyond devices that can run an agent. It now covers perimeter devices, cloud environments and applications, allowing teams to patch, isolate, uninstall or apply a custom fix across a broader hybrid attack surface. For assets that cannot run an agent, remediation is handled through scanners and existing security and IT integrations.
Another element of the release is the use of existing controls in the decision-making process. Qualys says TruConfidence first accounts for protections already active in a customer environment to avoid duplicate action. Where exposures remain, it identifies available compensating controls through third-party tools already used on endpoints and perimeter systems.
Operational risk
A central issue for patching teams is the risk that a fix will interrupt business operations. Qualys says TruRisk Eliminate monitors system health after remediation actions through integrations with partners including Dynatrace, checking for CPU spikes, memory issues and other signs of service impact.
If a fix fails or creates a problem, the product includes Patch Failure Analysis, which Qualys says explains the likely cause and suggests a corrective action such as a rollback. The feature is intended to reduce hesitation among organisations that want greater automation but remain concerned about outages.
Industry analysts say that concern reflects a broader change in how vulnerability management must operate. "For years, security teams found vulnerabilities and IT operations teams patched them. That handoff was built for exploitation timelines measured in weeks. With frontier AI, those timelines are now measured in hours, and neither team can close that gap alone," said Jon Nelson, Principal Advisory Director in the Security & Privacy Practise at Info-Tech Research Group.
"Qualys TruRisk Eliminate gives security a viable path to drive remediation at machine speed, with patch reliability scoring, progressive rollouts and patchless mitigation that reduce the risk of disrupting operations," Nelson said.
Qualys framed the product as part of a broader shift from vulnerability discovery to remediation execution. It argues that traditional workflows based on manual approvals, tickets and separate point tools were not built for the pace and complexity created by AI-assisted threat activity.
That change also affects the relationship between security teams and IT operations teams, which have often worked in sequence rather than through a single process. Qualys is using the new release to argue for a tighter operating model in which discovery, prioritisation and remediation are managed with more automation and fewer handoffs.
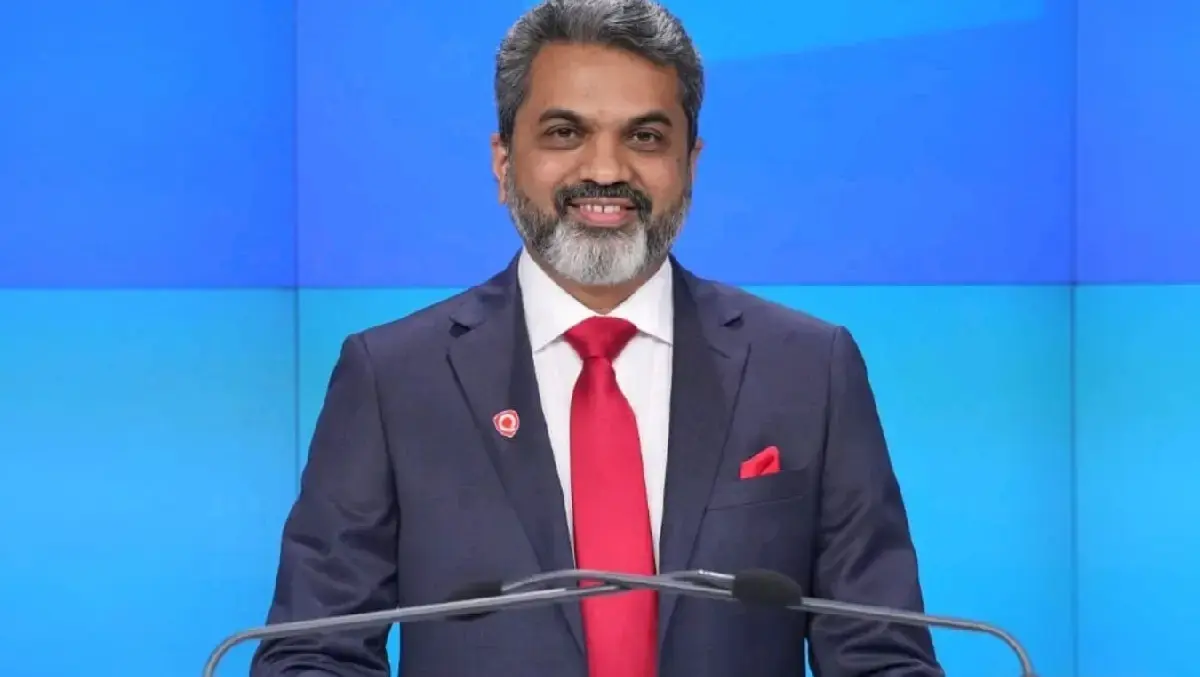
"Autonomous exploitation requires equally automated remediation, but organizations' hesitation isn't about automation, it's a lack of confidence that it won't cause an outage," said Sumedh Thakar, President and CEO of Qualys.
"That's why we're excited to introduce TruRisk Eliminate with TruConfidence, moving beyond patching to turn remediation intelligence into action with the Risk Operations Centre so organizations have the confidence to reduce cyber risk quickly while reducing outage concerns," Thakar said.