Security analytics stories
Microsoft security teams can now ingest email authentication signals in one place, helping spot phishing and spoofing sooner during investigations.
Fraud teams and AI builders can now query linked data in BigQuery without moving it to a separate graph database, Google said.
Security teams may miss threats if they judge AI only by speed, as low escalation rates can hide false dismissals and risk.
Investigators could gain a fuller view of insider risk as Proofpoint links Microsoft 365 messages and files with AI interactions.
Security teams under pressure from faster intrusions can now use Zscaler's new platform to spot and contain AI-driven attacks at machine speed.
Security teams are under pressure from faster AI-driven attacks, prompting Zscaler to add automated remediation and third-party integrations globally.
The new product aims to spot and contain malicious AI-agent activity in clouds as firms brace for faster, harder-to-detect attacks.
Analysts at Littlefish could assess threats in seconds or minutes as its new software trims alert backlogs without replacing human judgement.
Forrester said perimeter-only defences no longer suffice as industrial networks become more tightly tied to enterprise IT and cloud services.
Trusted employees and AI agents are now seen as prime insider risks, with deepfake fraud and hidden access gaps worsening the threat.
Security teams can now trace blocked cloud requests faster, as Google Cloud rolls out policy intelligence for VPC Service Controls to cut investigation time.
Security teams could get faster investigations as ClickHouse folds RunReveal's platform expertise into its database business.
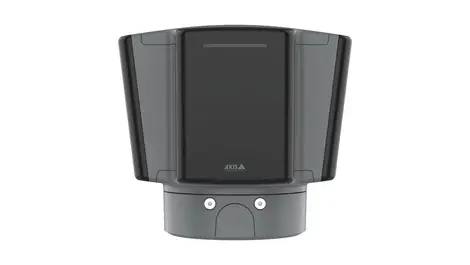
The system aims to cut false alarms and manual checks for operators guarding large, exposed sites in poor light or bad weather.
The tie-ups give customers more choice over where security data is processed, while easing procurement for joint CrowdStrike and Snowflake users.
Security teams could spot insider threats sooner as Exabeam joins Google's recommended partner programme for behavioural analytics tied to AI agents.
Security teams are finding that overlapping products can swamp alerts, raise costs and obscure whether defences are actually improving.
Apple's rare backported patches for older iPhones highlight how exploit kit tactics are also being used to hide fraudulent advertising campaigns.
Enterprise security teams could cut alert noise and speed response after the UK managed detection and response provider put RADAR into production.
Security teams could gain wider visibility into AI data flows as native Falcon support and two CrowdStrike integrations extend across VAST's platform.
Australian firms still face email compromise and poor security hygiene, even as AI helps criminals move faster and hide harder.